MALAYSIA’S rapid digitalisation is often celebrated as evidence of technological progress, administrative efficiency and economic modernisation.
Government services are moving online, businesses are embracing cloud computing, financial transactions are increasingly cashless, and public infrastructure is becoming interconnected.
Yet an uncomfortable question remains: are the systems supporting this transformation sufficiently secure, or are we expanding our digital dependence faster than our capacity to protect it?
Recent incidents in Europe demonstrate how ordinary digital systems can become unexpected points of vulnerability.
Euronews reported on Nov 3 that supermarket refrigeration systems in several European countries had been remotely compromised, causing some fridges and freezers to warm up and raising concerns about the security of internet-connected equipment.
The Guardian subsequently reported that France’s national blood service had experienced cyber interference involving temperature and defrosting controls at three storage facilities.
The attack targeted a refrigeration equipment supplier, rather than the blood service directly. Alarm systems detected the changes, allowing staff to intervene before any blood products were compromised.
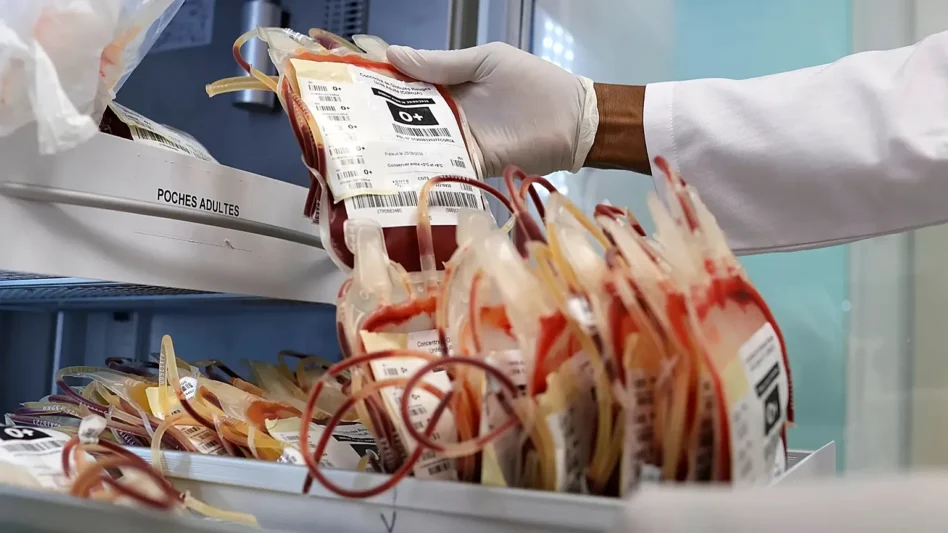
Although the incidents were contained, they demonstrate how compromised technology can threaten the reliability of everyday services.
Malaysia has its own warning signs. The hacking of several LED advertising screens in Kluang, Johor, which resulted in obscene content being broadcast publicly, might initially appear to be an embarrassing but relatively minor incident.
However, the more important issue is not the content displayed but the apparent ability of unauthorised individuals to gain control of remotely managed infrastructure.
The Kluang Municipal Council shut down the affected screens and said it was investigating the incident with its technology vendor.
This exposes a weakness that deserves considerably greater attention: the security of systems operated through third-party vendors.
Public authorities increasingly outsource technological infrastructure, including software management, cloud services, surveillance equipment and digital communication platforms.
However, outsourcing operational responsibilities does not mean outsourcing institutional accountability. If a vendor’s system is compromised, the organisation must still answer for the consequences.
More concerning is the possibility that similar weaknesses exist across other organisations. Internet-connected devices, commonly referred to as the Internet of Things (IoT), are increasingly integrated into building management, healthcare equipment, traffic systems, retail operations and industrial processes.
Some devices may be deployed with default passwords, inadequate authentication, outdated firmware or insufficient security updates.
Once connected to wider networks, these weaknesses can provide attackers with opportunities to access systems beyond the original device.
Malaysia’s cybersecurity statistics reinforce these concerns. CyberSecurity Malaysia recorded 2,715 incidents reported to its Cyber999 Incident Response Centre in the second quarter of 2026, compared with 2,188 in the preceding quarter, a 24.09% increase.
Reported data breaches rose by 41.13%, from 124 to 175, while fraud accounted for 2,314 incidents. These figures reflect incidents reported to and handled by the centre, rather than a complete count of all cyber incidents in the country.
The implications for ordinary Malaysians are substantial. Personal information held by government portals, financial institutions, telecommunications providers and commercial platforms forms an extensive digital footprint.
Identity card numbers, residential addresses, banking credentials and contact details can become valuable commodities when exposed through inadequate data protection.
A breach does not necessarily end when an organisation restores its systems. Stolen information may continue circulating, enabling identity theft, impersonation, fraudulent transactions and targeted scams.
The underlying problem is that cybersecurity is frequently treated as a technical responsibility rather than an organisational priority.
Installing antivirus software, purchasing firewalls or appointing an information technology officer does not automatically make a system secure.
Effective protection requires continuous vulnerability assessments, penetration testing, access restrictions, software updates, encryption and independent security audits.
Equally important are tested backup arrangements and recovery procedures. Organisations must be able to restore services without depending entirely on compromised systems.
Artificial intelligence adds another dimension. Cybercriminals can exploit AI to produce convincing phishing messages, automate reconnaissance and identify weaknesses across connected systems.
The challenge is therefore not simply preventing unauthorised access, but anticipating how vulnerabilities can be exploited at scale.
Malaysia already has a legislative framework through the Cyber Security Act 2024 and amendments to the Personal Data Protection Act 2010.
However, the Cyber Security Act’s requirements are particularly focused on designated National Critical Information Infrastructure entities, while the amended Personal Data Protection Act places obligations on organisations processing personal data in commercial transactions.
Regulatory compliance should not become a box-ticking exercise. Authorities must ensure that organisations demonstrate genuine security capabilities, rather than merely possessing policies and documentation.
Smaller businesses, local authorities and organisations relying on external technology providers also need technical assistance and resources to meet appropriate standards.
Ultimately, digital transformation must be accompanied by digital accountability. Government agencies and private organisations should disclose breaches responsibly, conduct regular independent assessments and establish clear accountability for failures involving vendors and service providers.
Cybersecurity standards must also extend to seemingly insignificant devices and platforms, not merely major databases.
Malaysia should measure its digital progress not by the number of applications introduced, services migrated online or transactions conducted electronically, but by the reliability and security of the systems supporting them.
Convenience without protection creates vulnerability. A digitally connected society is only as dependable as its weakest system. ‒ Nov 5, 2026
R Paneir Selvam is the principal consultant of Arunachala Research & Consultancy Sdn Bhd, a think tank specialising in strategic national and geopolitical matters.
The views expressed are solely of the author and do not necessarily reflect those of Focus Malaysia.
Main image: Tech Wire Asia