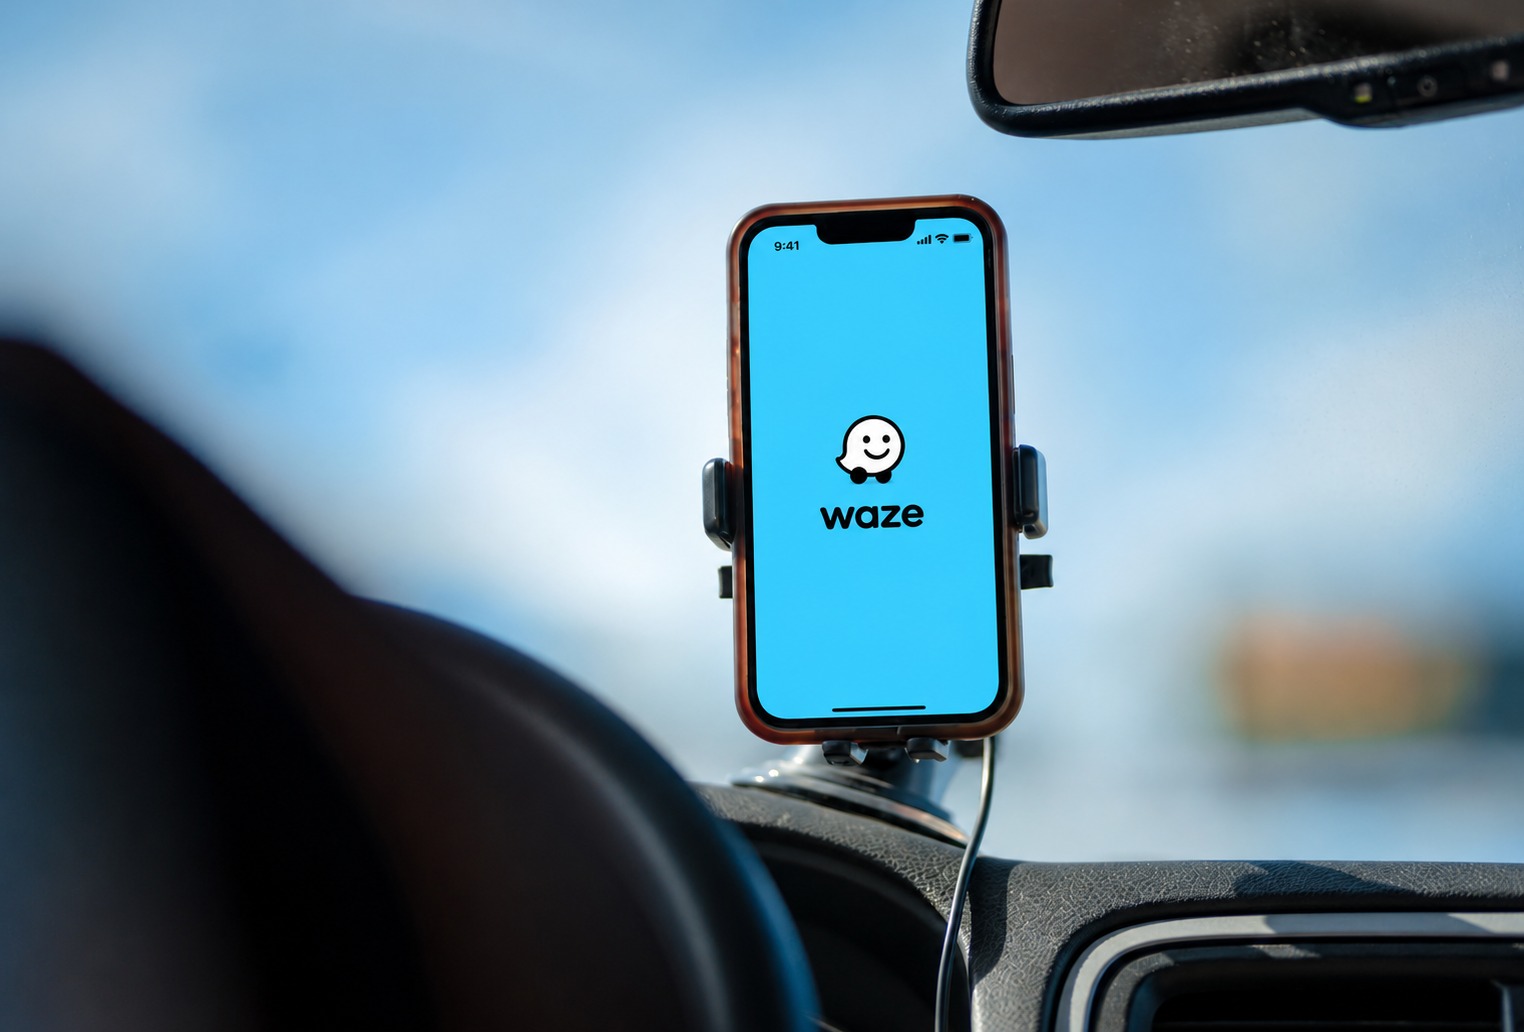
CAN a navigation application become a national security liability?
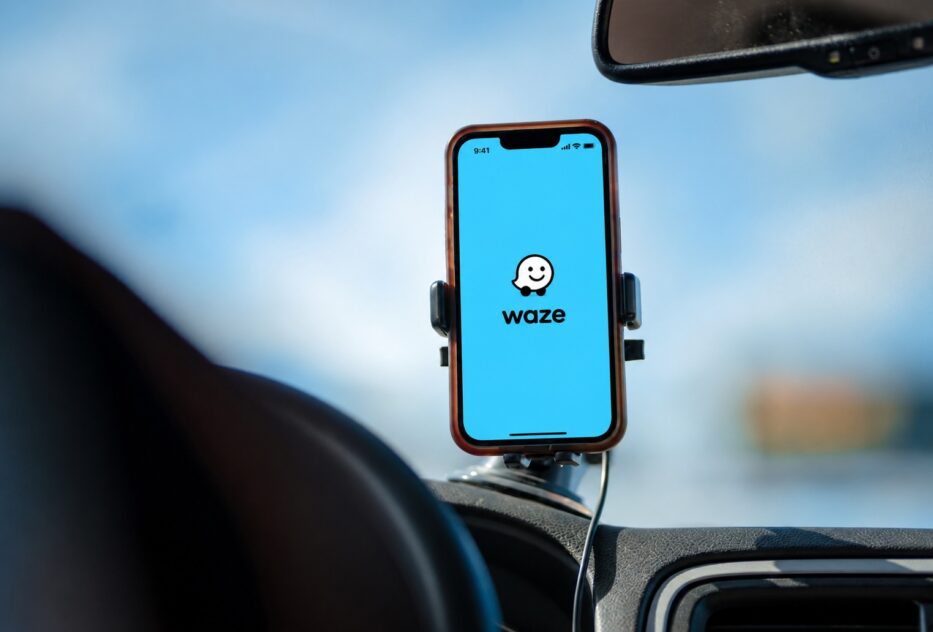
Malaysia’s decision to restrict civil servants’ use of Waze has brought an increasingly urgent question into public debate: who controls the digital information generated by technologies that governments and citizens use every day?
The concern is not simply about maps or directions. It is about data ownership, foreign legal jurisdiction and the possibility that information collected for commercial purposes could acquire strategic value.
Malaysia should treat the Waze controversy as an opportunity to build a coherent digital security policy, rather than regard an application ban as an end in itself.
When ordinary data becomes strategic
Waze relies on location information and user contributions to provide navigation and real-time traffic updates. While such information is useful for identifying congestion, repeated movement patterns may also reveal routines around government offices, security installations and critical infrastructure.
The wider implications were illustrated by a South China Morning Post report published in May 2026.
Citing testimony before a US congressional advisory commission, it described concerns that large-scale data collection could support intelligence gathering, economic competition and military planning.
The underlying lesson is that information collected for one purpose may acquire a different strategic value when aggregated and analysed.
This does not establish that Waze has been used for espionage. Indeed, Waze has rejected allegations that it collects sensitive government information or allows the exploitation of users’ personal data.
Malaysia must distinguish between a credible vulnerability, a potential threat and proven misconduct.
Nevertheless, governments cannot wait for a security breach before examining risks involving sensitive official activities.
The jurisdiction question
Malaysia’s National Cyber Security Agency (NACSA) has identified the application’s data collection practices and Israeli governing-law and jurisdiction clauses as concerns.
Such provisions raise legitimate questions about where disputes would be resolved and what practical remedies might be available to Malaysian users.
However, foreign jurisdiction alone does not prove that a company’s government can freely access all the information it processes.
The more useful questions are what information is collected, where it is processed, which parties can access it, how long it is retained and what legal safeguards apply.
The distinction matters because digital sovereignty cannot be measured simply by the nationality of a technology provider. It depends on whether Malaysia can establish enforceable protections over information relevant to its national interests.
What Malaysia should do
First, the government should clarify the scope of the Waze directive. Official communications have not been entirely consistent: the initial directive was described as applying to official government duties, while NACSA’s published FAQ states that the restriction applies to civil servants at all times, including personal use.
Clear and consistent guidance is essential for compliance, proportionality and public confidence.
Second, NACSA should coordinate a formal assessment framework for digital applications used in government.
Assessments should examine data permissions, overseas processing, third-party sharing, retention policies, contractual jurisdiction and the consequences of a potential compromise.
Applications used by personnel handling classified information should face more stringent requirements than those used for routine administrative tasks.
Third, Malaysia should establish a government-wide register of approved digital applications, supported by periodic independent security audits.
Agencies should have clear procedures for restricting high-risk services, reporting vulnerabilities and responding to suspected breaches.
Procurement contracts should provide enforceable protections for government information and require providers to disclose significant security incidents.
Fourth, Malaysia should strengthen its domestic digital alternatives without assuming that local ownership guarantees security.
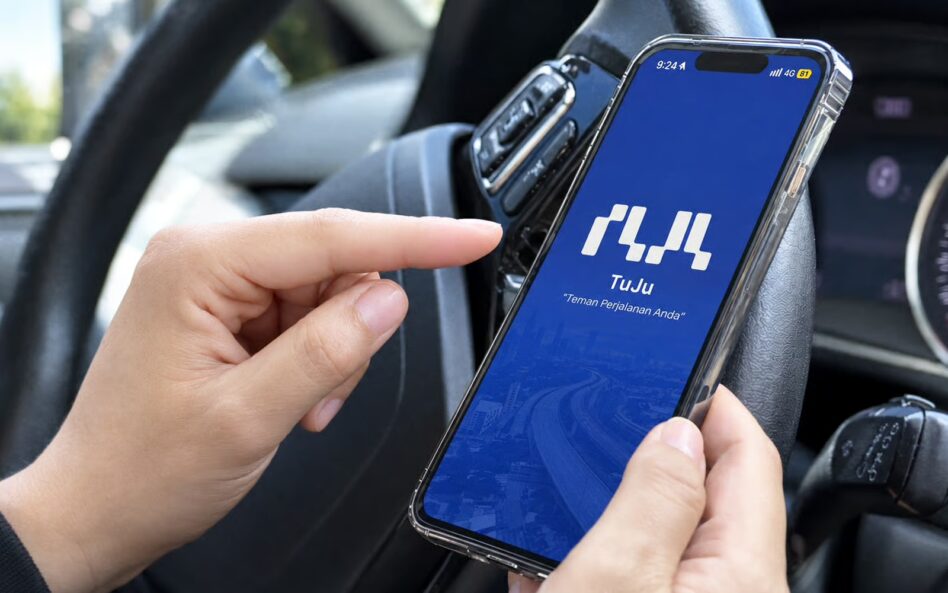
TuJu, developed by the Malaysian Highway Authority in collaboration with Prosignal Consortium Sdn Bhd, could form part of the national response.
However, its reliability, privacy safeguards, technical resilience and ability to meet users’ needs must be independently assessed. A replacement that performs poorly may discourage adoption and undermine the policy’s objectives.
Finally, the government should apply consistent standards across digital services, including navigation platforms, cloud systems and other applications that process sensitive information.
Restrictions should be based on demonstrable risks, with clear criteria, periodic review and appropriate oversight. Otherwise, security policy risks becoming selective and difficult to defend.
From prohibition to preparedness
Malaysia’s position on Palestine and its broader foreign policy may shape how it evaluates relationships with foreign entities. Yet national cybersecurity requires a framework capable of distinguishing political considerations from technical evidence and legal risk.
The Waze controversy should therefore trigger a broader examination of how government agencies manage digital dependencies.
The objective is not to reject foreign technology indiscriminately, but to ensure that its use does not compromise sensitive operations or leave Malaysia without effective remedies.
A ban can reduce exposure to a particular service, but it cannot substitute for institutional preparedness.
Malaysia must move from reacting to individual applications towards a digital security regime built on independent assessment, enforceable safeguards and consistent accountability.
Sovereignty in the digital age is not merely the freedom to prohibit a technology; it is the capacity to understand, govern and protect the information on which national security depends. ‒ Oct 30, 2026
R Paneir Selvam is Principal Consultant at Arunachala Research & Consultancy Sdn Bhd (ARRESCON), a think tank specialising in strategic national and geopolitical analysis.
The views expressed are solely of the author and do not necessarily reflect those of Focus Malaysia.
Main image: Scoop.my