HOME broadband connections are now being bombarded by automated cyber probes as hackers use artificial intelligence and low-cost tools to search indiscriminately for vulnerable Internet addresses.
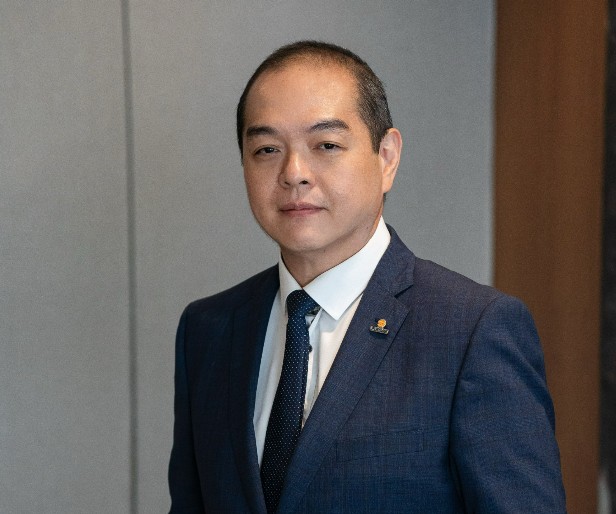
Unlike corporate targets, attackers no longer need to select victims individually, according to LGMS Bhd founder Fong Choong Fook.
“Automated systems can scan thousands of connections continuously, looking for weak router settings, outdated software and exposed devices,” revealed Fong who is also managing director of the cybersecurity outfit.
“The growing number of smart televisions, security cameras, doorbells and other Internet-connected appliances also provides more possible entry points.”
Hackers may be seeking online banking and e-mail credentials, personal data or access to cameras and other connected devices. A compromised router or household device can also be added to a botnet and used to spread malware, send spam or launch attacks on other targets.
Fong went on to share that a monitoring system installed on his home network typically detected between 500,000 and 650,000 probes and attempted attacks a day. His latest daily report recorded about 625,000 such events.
Stressing that the figure did not mean his home network had been successfully breached, he said the detections included automated scans and attempts to identify connected systems with exploitable vulnerabilities.
More broadly, the numbers simply showed that home users and businesses are now exposed to the same global threat environment.
‘AI is a double-edged sword’
“Attackers really don’t care who we are. They only care whether they can find a loophole, get your data or disrupt your business and hold you to ransom,” he observed, adding that automated tools and AI (artificial intelligence) have sharply reduced the cost and effort required to launch cyber-attacks.
“The speed and volume had also reached a level that could no longer be handled through human monitoring alone,” he asserted further. “If we use humans to analyse all this, there’s no way they can go through everything. Somehow, you have to resort to machines.”
AI could perform the initial assessment of security alerts, separating routine probes from serious or targeted activity before escalating critical cases.
Organisations should also establish clear policies determining how an alert was assessed, who should be contacted and when an incident-response plan should be activated.
Fong warned that the period between the disclosure of a software vulnerability and its exploitation by attackers had fallen from about 2.3 years in 2018 to less than a day in 2026. This left companies with little time to test security updates and obtain approval before installing them.
“Unfortunately, we don’t expect hackers to submit change requests before they exploit our systems,” remarked Fong.
“AI is a double-edged sword: It could help defenders review software, analyse security data and respond more quickly while allowing attackers to discover vulnerabilities and operate continuously.”
As such, he contended that cybersecurity could no longer be regarded solely as an information technology matter.
“It’s a business, legal, marketing and public relations issue altogether.”
On this note, Fong urged organisations to identify the AI technologies being used internally, establish clear policies governing their use and monitor their behaviour continuously.
LGMS recorded about 110% growth in its incident-response business in its 1Q FY2026 compared with the corresponding period last year, indicating that more organisations were seeking help to contain, investigate and recover from cyber incidents. – Oct 7, 2026
Main image credit: AIBP